Varaxon Scan Hub Brings Scanner-Agnostic Reporting and Remediation Tracking to MSPs
Nov 19, 2026
Managed service providers can use the scan files and assessment reports clients already have, turn findings into remediation tickets, and show what was fixed at the next quarterly business review.
United States, November 19, 2026 -- Varaxon Technologies LLC has launched support for importing existing security assessment PDFs into Varaxon Scan Hub. Managed service providers (MSPs) can review findings from penetration tests, prior vendors, and other assessments, then use those findings as a baseline for tracking what later scans show was fixed. MSPs can use the same reporting and remediation workflow across clients that use different scanners, without asking those clients to switch tools.
Start with the scans and reports the client already has
One client might send a Nessus export, another might use Qualys, and a third might hand over a PDF from its previous IT provider. Scan Hub reads supported exports from tools including Tenable Nessus, Qualys, Rapid7, Greenbone/OpenVAS, Nuclei, and Burp Suite. It also supports direct connections to Microsoft Defender and ConnectSecure. For structured exports, what matters is whether the CSV, XML, or JSON file contains the findings Scan Hub needs, not whether the MSP owns the scanner that produced it.
The scan-file preflight check lets a team see whether an export is readable, what hosts and findings it contains, and where information is missing. It requires no account and does not use a report credit. Teams can upload supported older scan exports or start with findings from an existing PDF, such as a penetration test, security assessment, or prior vendor report. For text-based PDFs, the platform identifies candidate findings by page, and a technician confirms which ones go into the report and the client’s history.
Turn findings into work the team can track
Before ranking a finding, Scan Hub checks what the scan can reliably tell the team. When the export includes the relevant metadata, it checks the scan date and plugin feed age, flagging stale results or outdated scanner checks. It also checks the support status of software versions identified in the scan, flagging versions that have reached end of life when lifecycle data is available.
Scan Hub then cross-references the vulnerabilities reported by the scanner with CISA’s Known Exploited Vulnerabilities catalog, VulnCheck KEV, FIRST’s Exploit Prediction Scoring System (EPSS), official CVE records, NIST’s National Vulnerability Database (NVD), and other relevant sources. These checks help distinguish confirmed exploitation, predicted likelihood, and technical severity. When data is missing or sources conflict, the report makes that uncertainty visible.
Scan Hub produces a report under the MSP’s branding, with a plain-language executive summary and a prioritized fix plan backed by the scan evidence. When several findings share a fix, Scan Hub can group them into one action. Technicians review the proposed actions before sending them to ConnectWise PSA or HaloPSA as service tickets.
“MSPs shouldn’t have to tell a new client to change scanners just so the reporting works,” said Brandon Sooknanan, founder of Varaxon Technologies. “The team should be able to start with the evidence the client already has, give technicians a clear fix list, and come back next quarter with something that shows what changed.”
Show proof of fix at the next client review
When the next comparable scan is imported, Scan Hub compares it with earlier results to show what is new, what is still open, what has returned, and what the rescan supports marking as fixed. A closed ticket records the team’s work; a comparable rescan provides evidence of whether the finding is still present.
The client’s scan and remediation history also feeds a branded quarterly business review (QBR) PDF. It shows verified fixes, changes in open findings, overdue work, accepted risks, and priorities for the next quarter. That gives the MSP and its client a record they can use to discuss what the team accomplished, what still needs approval, and where to spend the next maintenance window.
Varaxon also offers public security tools that don’t require an account, including a CVE lookup, a list of known exploited vulnerabilities, and checks for SPF, DKIM, DMARC, and mail routing. These tools give technicians a way to answer a specific question without generating a full client report.
About Varaxon Technologies
Varaxon Technologies LLC develops Varaxon Scan Hub, vulnerability reporting and remediation tracking software for managed service providers, security consultants, and IT teams.
Contact Info:
Name: Brandon Sooknanan, Founder
Email: Send Email
Organization: Varaxon Technologies LLC
Address: United States
Website: https://varaxontech.com
Release ID: 89210137
Should any problems, inaccuracies, or doubts arise from the content contained within this press release, we kindly request that you inform us immediately by contacting [email protected] (it is important to note that this email is the authorized channel for such matters, sending multiple emails to multiple addresses does not necessarily help expedite your request). Our dedicated team will promptly address your concerns within 8 hours, taking necessary steps to rectify identified issues or assist with the removal process. Providing accurate and dependable information is at the core of our commitment to our readers.

Before you add AI to your product, fix how work moves inside the company
Most software and services companies ask the AI question in the same way: how do we add AI to what we sell? It sounds strategic. It sounds visible. It sounds like the kind of move a modern company should make. But for many businesses, it is not the best first move. The more practical starting […] The post Before you add AI to your product, fix how work moves inside the company appeared first on e27.

The crypto hype cycle is dead. Here are the 4 narratives replacing it
The fatigue you diagnosed is structural, not cyclical. The sector has run out of patience for projects that promised user utility and delivered clunky interfaces, empty virtual worlds, and speculative profile pictures. Play-to-earn gaming collapsed under unsustainable incentives. Metaverses remained ghost towns. Generic PFP NFTs lost their cultural premium. The first generation of real-world asset […] The post The crypto hype cycle is dead. Here are the 4 narratives replacing it appeared first on e27.

DOJ charges Russian national with spying on workers for 'large' defense tech company
Federal prosecutors charged a Russian national with secretly working for Moscow to conduct illegal surveillance of employees at a major defense technology company over Ukraine’s use of its technology in the war against Russia, the Justice Department announced Wednesday. Igor D’iu, who was arrested Oct. 30, allegedly followed workers, tracked down their home addresses and...
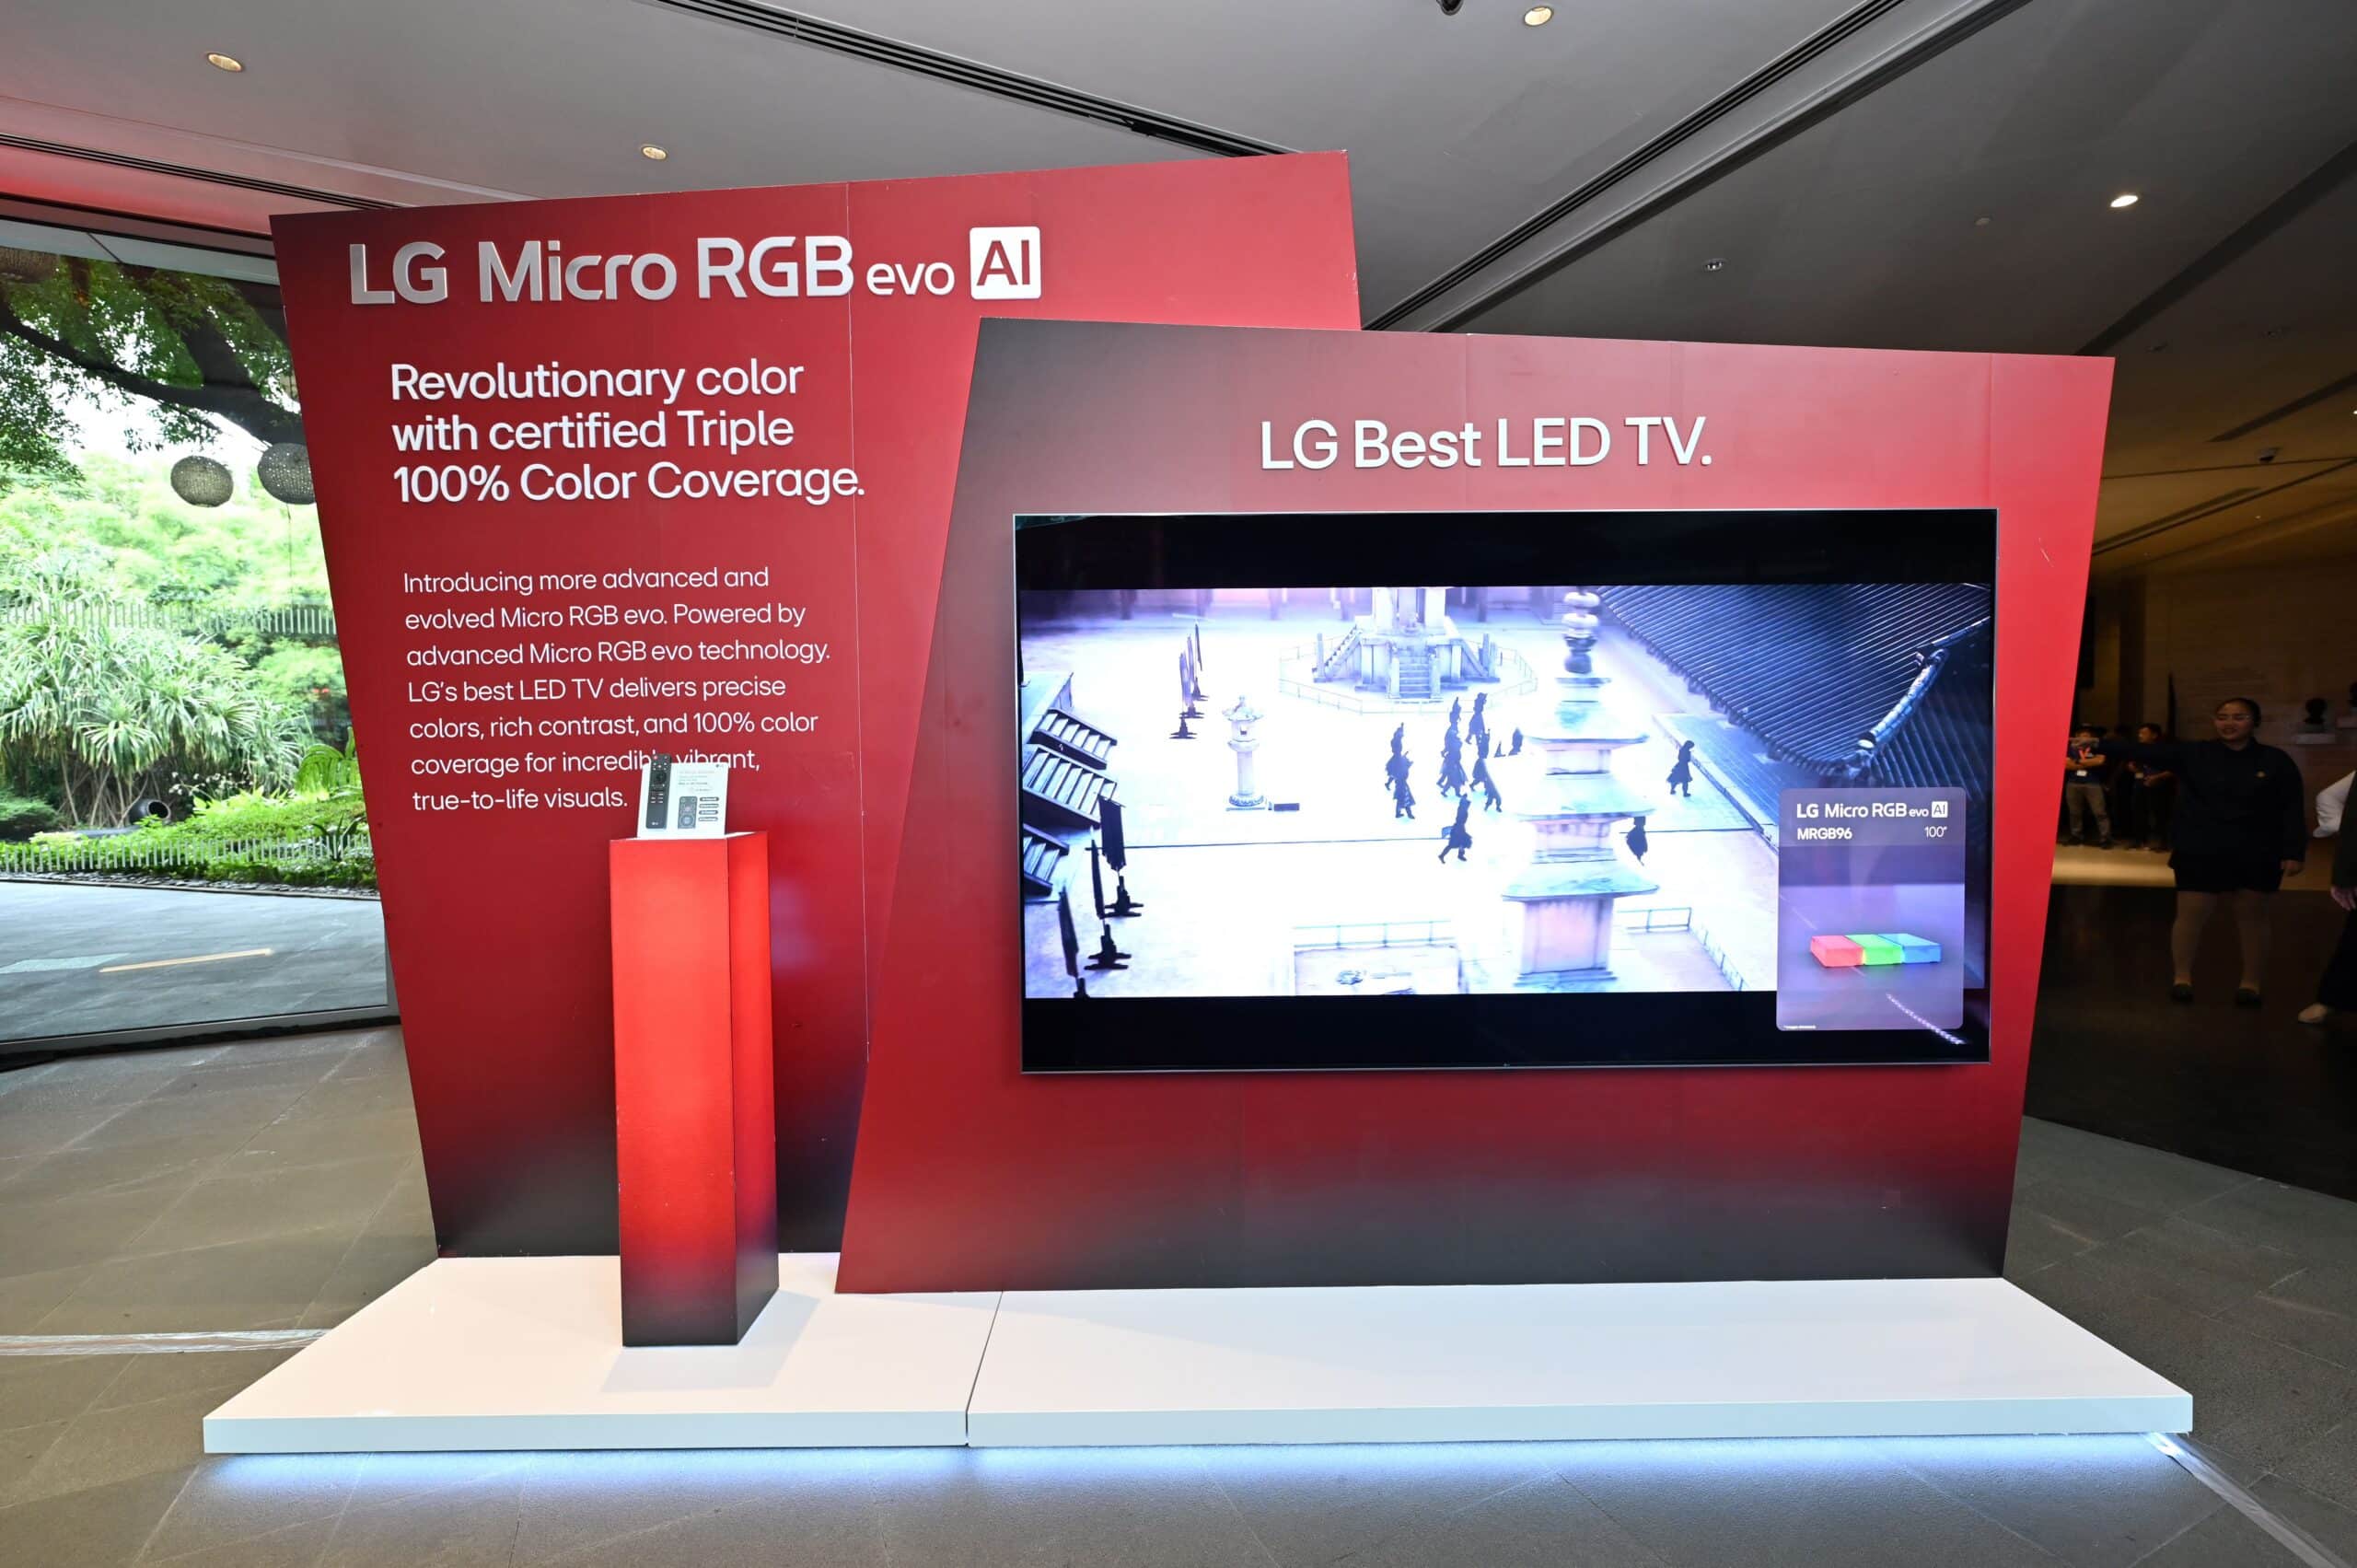
TV buyer’s guide for the holidays: OLED, micro RGB, QNED, LCD?!
Buying a TV used to be very straightforward. In the past, knowing how far your couch was from the television mount was enough information to determine how many screen inches your TV should be. In these modern times, that is no longer the case. The LCD panel of yore has evolved into its different iterations

Users report PlayStation issues hours before ‘GTA VI’ drop
“GTV VI” is scheduled to release at midnight on Thursday, though players in some parts of the world were already granted access as midnight arrived in their regions.

Former cybersecurity director: Tech outages 'ultimately a good news story'
Chris Krebs, the former director of the U.S. Cybersecurity and Infrastructure Security Agency, on Wednesday said that the recent spate of technology outages from the past week are "ultimately a good news story." "I know it kind of sucks in the moment when you can't access your app or your flights are delayed, but we're...

Cybersecurity expert: 'There will be a significant ramp up in incidents'
Jen Easterly, the former director of the U.S. Cybersecurity and Infrastructure Security Agency, on Monday warned that the U.S. will likely see a "significant ramp up" in incidents involving digital infrastructure, including outages and cyber threats. "We have to be prepared for disruption, because disruption is going to occur, so we need to plan for...

Britt proposes creating national office to address financial fraud
GOP Sen. Katie Britt (Ala.) on Wednesday introduced legislation to create a national office dedicated to fighting financial fraud and scams. Britt’s bill proposes forming a National Office for Scam and Fraud Prevention within the White House. That bureau would develop a “comprehensive national strategy and strengthen coordination” among federal agencies, financial institutions and technology...

House panel requests briefings from interim Nvidia CEO, Lutnick
Rep. Brett Guthrie (R-Ky.), chair of the House Energy and Commerce Committee, sent letters to interim Nvidia CEO Colette Kress and Commerce Secretary Howard Lutnick Wednesday, asking them to appear before the panel as scrutiny into both grows in Washington. Guthrie’s letter called on Kress, who's been a top Nvidia executive for over a decade,...
Grand Theft Auto: the evolution of a controversial franchise
MANILA, Philippines – This month of November, Grand Theft Auto (GTA) VI, one of the most highly anticipated games will finally be released on PC and modern consoles after over a decade of teases, delays, and outright controversy. As the eighth mainline entry in Rockstar Games’ action-adventure open world video game series, GTA VI is

Cyberattack hits 178 websites, targets older Apple devices
MANILA, Philippines – Hackers recently targeted 178 websites with a malicious cyberattack designed to steal financial information and infect older Apple devices. Attackers injected malware into Optimizely, a platform used by major companies such as BBC, CNN, IKEA, HSBC, and Zoom. They embedded malicious JavaScript in Optimizely to steal card details. The code also exposed

Pence: Lutnick 'may need to go'
Former Vice President Mike Pence said he believes Commerce Secretary Howard Lutnick “may need to go” following criticism over his handling of Nvidia's sale of advanced AI technology to China and an alleged honey trapping scheme targeting the firm's former CEO, Jensen Huang. Appearing on CNN’s “The Source” Tuesday, host Kaitlan Collins asked Pence on...


YOUR NEWS, OUR NETWORK.
Do you have Great News you want to tell the world?
Be it updates about your business or your community, you can make sure that it’s heard by submitting your story to our network reaching hundreds of news sites across 6 verticals.